
Director of Nationwide Intelligence Jay Clayton mentioned Tuesday that technical points impacting the Nationwide Safety Company and different areas are usually not the results of a cyberattack or state-sponsored exercise, amid cybersecurity issues over reported outages.
“This isn’t a cyberattack, and this isn’t a coordinated effort by a nation-state,” Clayton mentioned throughout an interview with CNBC on Tuesday when requested about latest reported tech outages within the authorities and personal sector.
“We have regarded very intently. Anytime we see one thing like this, these are the primary questions that we ask on behalf of the American folks. And we go throughout and we are saying, ‘Is that what is going on on right here?’ That’s not what is going on on right here,” he mentioned.
Clayton’s feedback got here the identical day Secretary of State Marco Rubio additionally sought to assuage fears over latest high-profile expertise failures and repair disruptions, giving the Trump administration’s clearest declaration that the occasions are “utterly unrelated” and had “nothing to do with a cybercriminal has nothing to do with a hostile actor or one other nation.”
“We aren’t beneath systemic assault,” Rubio informed reporters.
The secretary acknowledged that the failures had been “unsettling,” however mentioned they may very well be blamed on run-of-the-mill pc errors.
“Every of them are distinct, and so they’re totally different of their causation,” he mentioned.
In one other interview on Fox Enterprise on Tuesday, Clayton mentioned he was “pretty assured” in his assertion as a result of “we all know these issues exist and we’ve got been in search of them prior to now.”
Clayton’s feedback come after an inside communications system utilized by NSA workers to share labeled info briefly went down on Tuesday. The NSA mentioned the community points occurred throughout “scheduled routine upkeep” and that “mission-critical capabilities stay absolutely operational and our skill to defend nationwide safety continues.”
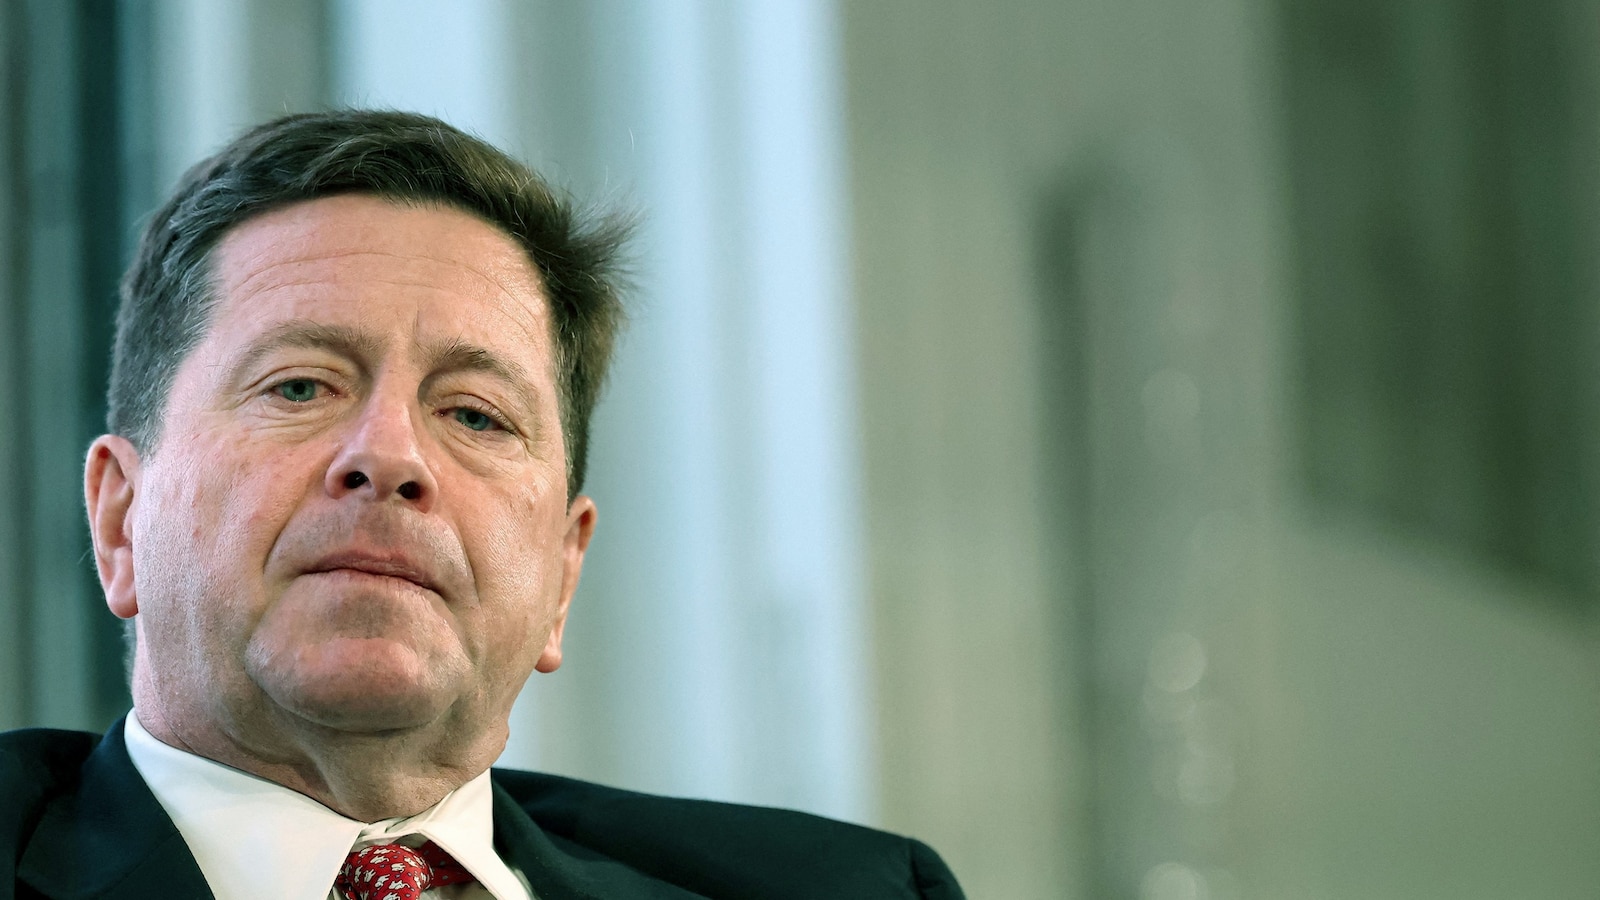
Jay Clayton, Director of Nationwide Intelligence, attends the 13D Monitor’s Lively-Passive Investor Summit in New York, Oct. 20, 2026.
Brendan Mcdermid/Reuters
Clayton informed Fox Enterprise that what the administration is pretty assured has been taking place is that expertise programs throughout establishments are upgrading and “patching” the place vulnerabilities have been discovered, together with on the NSA.
“As you patch and improve your programs, taking them down and bringing them again up, there are issues like this that occurred,” he informed CNBC.
“We can have different patches going ahead as we improve our infrastructure. However this isn’t one thing that may be a coordinated cyberattack or a state-sponsored effort in opposition to the U.S.,” he continued.
Clayton, who additionally chairs the White Home Tremendous Intelligence Drive (the Trump administration’s time period for synthetic intelligence), informed Fox Enterprise that AI is ready to scan programs “extra rapidly,” and consequently, “the flexibility to determine vulnerabilities has elevated.”
“That’s the reason it’s so incumbent upon all of us to work collectively, to patch, to report vulnerabilities,” he mentioned.
Sen. Mark Warner, D-Va., vice chairman of the Senate Choose Committee on Intelligence and co-chair of the Senate Cybersecurity Caucus, echoed Clayton’s remarks in an announcement on Tuesday.
“I perceive why People are involved in regards to the widespread outages we have seen in latest days, affecting every little thing from banks and main expertise corporations to important authorities programs. At this level, there isn’t a indication that these incidents are the results of a cyberattack, international interference, or some coordinated effort,” he mentioned.
Warner additionally pointed to synthetic intelligence, saying AI is “making it potential to determine vulnerabilities throughout huge numbers of programs at unprecedented velocity, creating huge strain on corporations and authorities businesses to patch these vulnerabilities instantly, typically unexpectedly, placing super pressure on programs that weren’t constructed to deal with that tempo of change.”
“Whereas we nonetheless have to resolve these incidents, the proof to date factors towards legit efforts to safe our programs, not malicious exercise,” he mentioned.
