
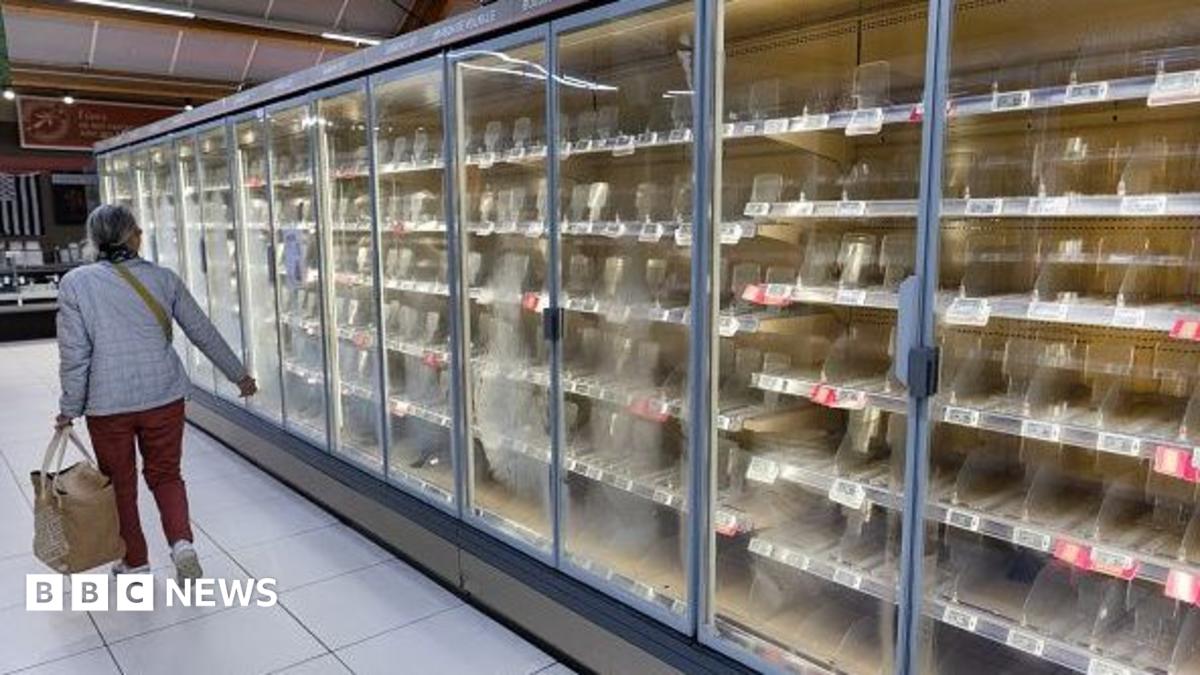
Supermarkets throughout Europe have been hit by a suspected cyber-attack affecting their fridges and freezers, and elevating concern concerning the vulnerabilities of internet-connected {hardware} from industrial equipment to humble home home equipment.
Good gadgets that are related to the web can embrace fridges, central heating, and even washing machines.
And whereas that makes them simpler to manage remotely, in principle, any machine which matches on-line can probably be exploited by malicious actors.
Nonetheless, that does not imply hackers can simply take management of it, and large manufacturers usually go to nice lengths to verify their tech is safe.
Exploits have been discovered earlier than in some gadgets. In 2015, researchers demonstrated how a vulnerability in a Samsung sensible fridge may permit them to intercept web visitors.
However there is no proof home home equipment are being focused within the cyber-attacks which focused supermarkets in November.
Ciaran Martin, former chief govt of the UK’s Nationwide Cyber Safety Centre (NCSC) says producers wanted to do extra to make related gadgets safe.
“There’s much more that we have to demand of massive tech to present us safer gadgets and merchandise within the first place,” he stated.
He suggested customers to maintain gadgets up to date and allow multi-factor authentication wherever attainable.
“I do know it is a ache, however it solely takes a number of seconds,” he stated.
Since April 2024, UK regulation has required producers of sure client sensible gadgets to satisfy minimal cyber safety requirements, together with necessities round passwords and safety updates.
The NCSC stated it was working with worldwide companions and business to grasp the grocery store incidents, however it was unaware of any affect on the UK.
Nonetheless, researchers from UK Cyber Defence have recognized greater than 800 refrigeration and building-control interfaces related to British retailers that may be accessed over the general public web.
That does not essentially imply they are often hacked, however it may depart them uncovered to attackers exploiting weak passwords or software program vulnerabilities.
The federal government has already held talks with senior meals retailers about cyber resilience, following earlier assaults on supermarkets.
Helen Dickinson, chief govt of the British Retail Consortium, has stated cyber incidents are a serious concern for retailers, with companies working alongside the NCSC to share intelligence and strengthen their defences.
It could not be the primary time that hacks have raised concern about affect on meals provide.
When UK supermarkets M&S and the Co-op had been focused by ransomware hackers in Could 2025, the retailers struggled to stock some shop shelves with contemporary deliveries.
Clients throughout the UK complained of empty shelves within the days following the assault.
Tom Hegel, a researcher at cyber-security agency SentinelOne, stated retailers should be clearer about accountability.
“The query retailers must reply is who owns the safety of that gear, not simply who repairs it,” he stated.
He stated web connectivity could make on a regular basis expertise extra handy, however safety wanted to maintain tempo.
“As soon as an attacker can function these controls, respectable capabilities similar to defrosting grow to be instruments for disruption,” he stated.
“Altering a setting can destroy bodily inventory, not simply interrupt a pc system.”
