
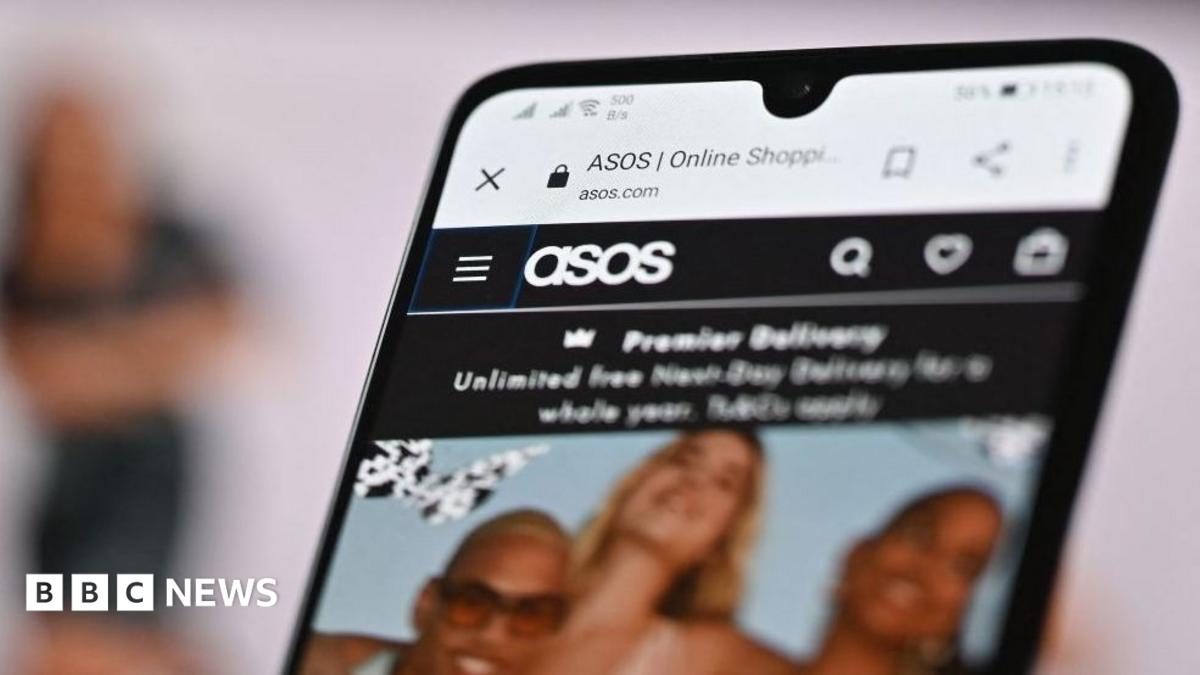
On social media, dozens of individuals have posted about receiving the message – confused as to what it means.
Though the obvious extortion message has been issued on to clients, it’s addressed to Asos’ information safety officer (DPO) and IT workforce.
The message claims the unnamed hackers have “absolutely compromised the Snowflake occasion”.
This refers back to the information storage firm Snowflake, whose instruments are utilized by dozens of companies for gathering, analysing and storing information.
It isn’t identified if ASOS is a buyer of Snowflake or what information, if any, is saved with the service.
However Snowflake has been the topic of many excessive profile information breaches lately and has been linked to incidents concentrating on companies together with Ticketmaster and Santander.
It’s, nonetheless, very uncommon for a knowledge breach to be revealed fairly so publicly – and for patrons to learn on this method.
Most extortions and negotiations by cyber criminals are carried out in personal, with hackers hoping their discretion will lead to a quiet pay-off.
The pop up message comprises a hyperlink to the hackers’ Telegram channel.
The brand new group is looking itself Xuanye Group and solely created its Telegram channel at present.
They’ve posted solely thrice with the newest being concerning the ASOS hack.
Dan Fowl, from cyber safety agency Horizon3 says the pop up message the criminals despatched implies that their entry has gone past the Snowflake database.
“Sending a push notification to ASOS’s app customers would require entry to the corporate’s notification system, which is separate from the Snowflake information platform the attackers declare to have compromised.”
“If each claims maintain up, it suggests the attackers obtained maintain of credentials that opened a couple of door,” he stated.
